Features
Locks on the doors that are actually used
Mail servers are attacked through credentials, not through clever exploits. The defences here are the ones that match how it actually happens.
Credentials
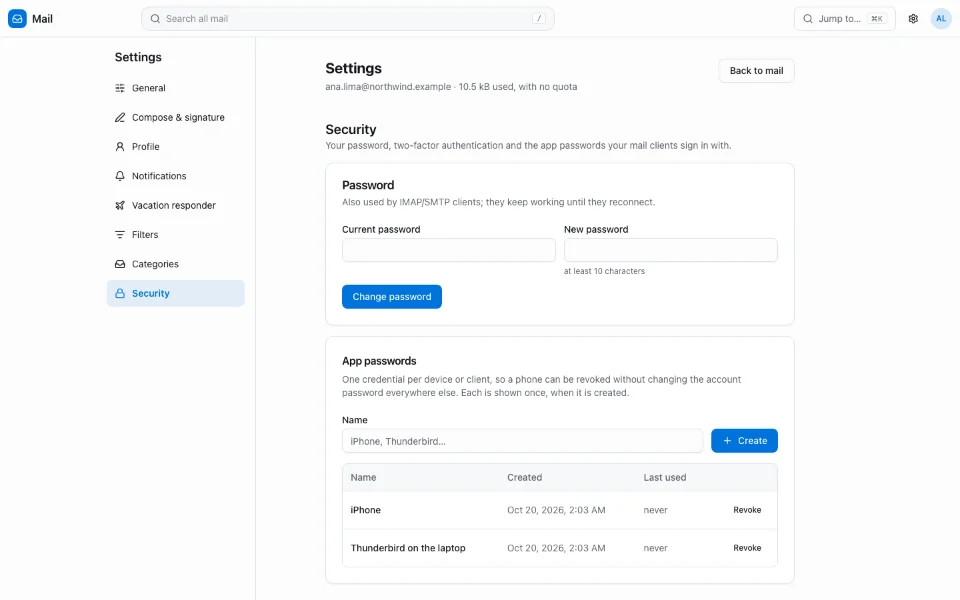
Mailbox users get TOTP on webmail sign-in, and app passwords for mail clients, which turning TOTP on makes mandatory — with single-use recovery codes, so a lost phone is not a lost mailbox. Administrators get three roles — owner, admin and domain admin — and their own TOTP. API access is a scoped token, not a password.
- App passwords per client
- TOTP for mailboxes and for admins
- Recovery codes for mailbox two-factor
- Three admin roles
- Scoped API tokens
When someone tries anyway
Failed logins are counted and banned at both surfaces — the API and the mail daemons read the same ban list, so a bot that gives up on the web form does not simply move to IMAP.
- One ban list, read by the API and by Dovecot
- Login rate limiting on both surfaces
When an account is already lost
A mailbox sending spam is contained automatically: sending is blocked, receiving is not. That distinction is deliberate — cutting off receipt punishes the victim for being compromised, and it is the customer’s mail either way.
- Containment blocks sending only
- The mailbox keeps receiving
At rest
Provider keys and migration credentials are encrypted with a server key, and from 0.11.0 so are DKIM private keys and the outbound relay password. TLS is Caddy’s ACME by default or your own certificate, synced to the daemons within thirty seconds either way.
- Secrets encrypted at rest
- ACME or bring-your-own TLS
In the browser and the containers
From 0.10.0, both applications send a content security policy and standard security headers, the sign-in routes refuse another origin, the web container runs unprivileged on a read-only filesystem, and every image we build is patched and scanned before a release pushes it.
- CSP and security headers
- Unprivileged, read-only web container
- Images patched and scanned before release
More
Where these claims come from
Each line on this page is backed by a document in the product’s own repository. They are private, so the paths are given rather than linked; ask us if you want to see one.
- mailserver · docs/feature-docs/security-baseline.md
- mailserver · docs/adrs/0007-control-plane-auth.md
- mailserver · docs/adrs/0017-secrets-encrypted-at-rest-with-a-server-key.md
- mailserver · docs/adrs/0016-compromised-mailbox-containment-blocks-sending-only.md
- mailserver · docs/adrs/0029-authentication-bans-are-one-table-both-surfaces-read.md
- mailserver · docs/feature-docs/app-passwords-and-mailbox-2fa.md
- mailserver · docs/feature-docs/login-rate-limiting.md